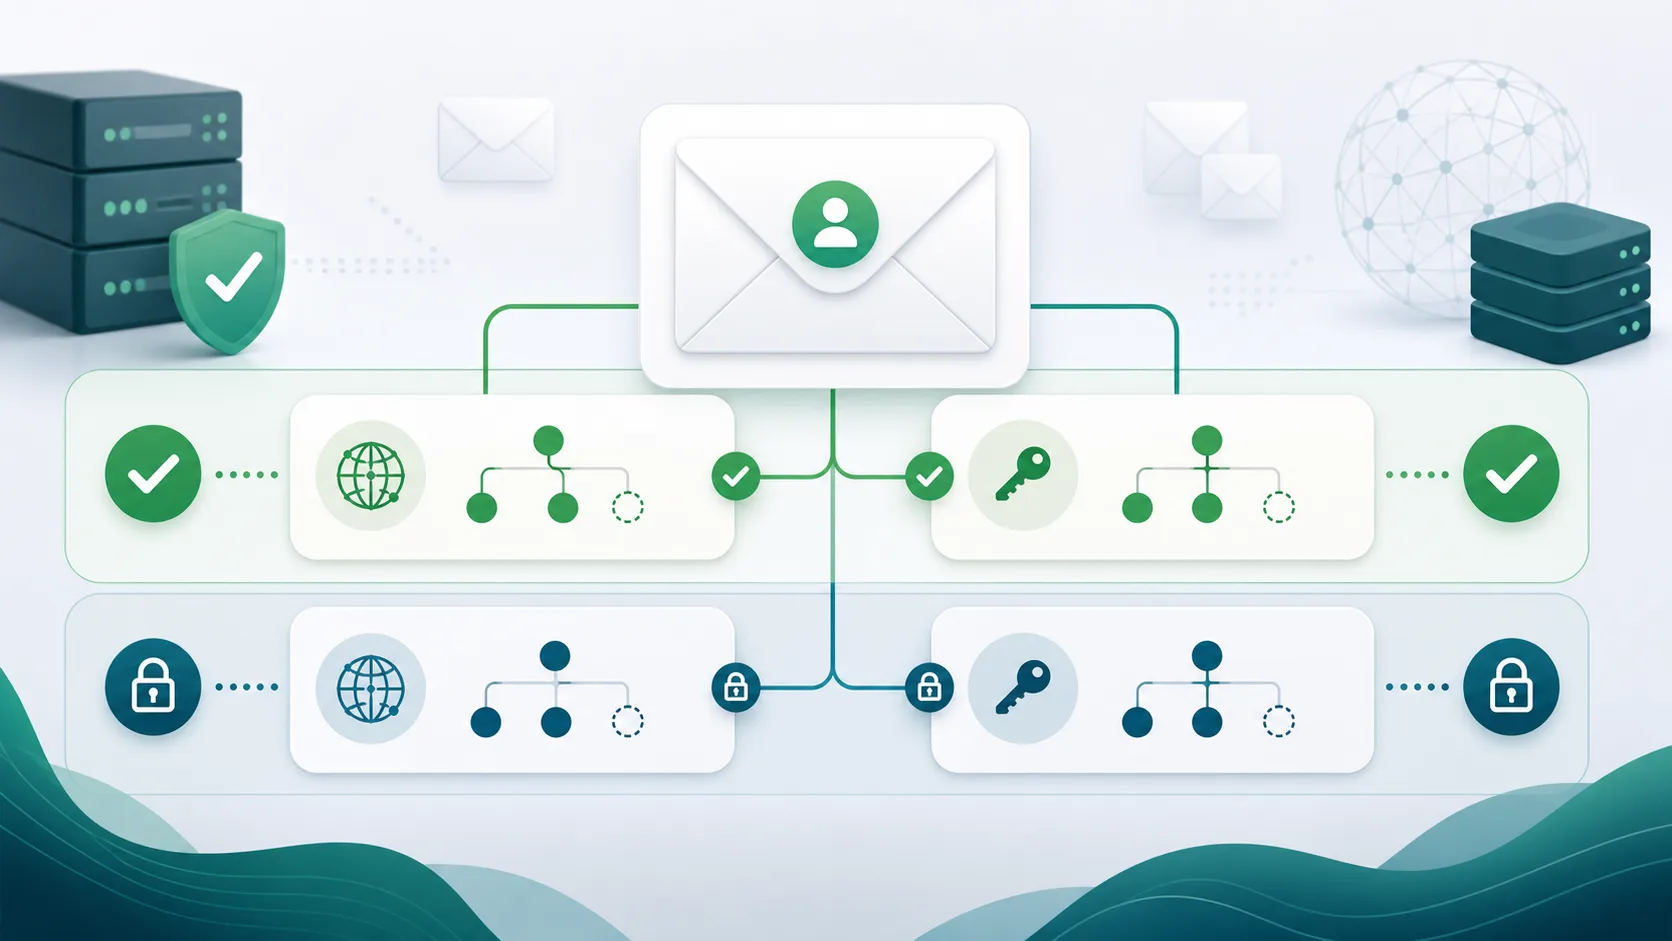
Relaxed alignment is the DMARC default for good reason: it lets legitimate subdomain-based mail streams pass while still tying authorization to the same organizational domain. Strict alignment is useful only after reports prove every legitimate sender can match the exact From domain.
DMARC is often described as “SPF plus DKIM plus a policy.” That shortcut misses the part that makes DMARC useful against spoofing: identifier alignment. A message can pass SPF. It can pass DKIM. It can still fail DMARC if the domain that passed is not aligned with the domain people see in the visible From header.
RFC 9989 keeps this idea at the center of DMARC. The author domain is the domain in the RFC5322.From header. DMARC passes only when at least one authenticated identifier lines up with that author domain. Alignment is where many “but SPF passed” investigations finally become clear.
The two identifiers DMARC compares
DMARC looks at two authentication paths. For SPF, the relevant domain is the validated MAIL FROM identity, also called the return-path or envelope sender. For DKIM, the relevant domain is the d= value in a validated DKIM signature.
The visible sender is different. It is the domain in the From header that a recipient usually sees in the mail client. DMARC asks whether the SPF domain or DKIM signing domain is aligned with that visible author domain.
Visible From:          billing@example.com
SPF MAIL FROM:        bounce@mail.example.com
DKIM d= domain:       example.com

DMARC passes if either SPF or DKIM passes and the passing domain aligns with example.com.
Relaxed alignment is the default
The alignment tags are aspf for SPF and adkim for DKIM. If you do not publish them, both default to relaxed mode. In relaxed alignment, the domains do not have to be identical. They have to share the same organizational domain.
That default matters because real mail streams commonly use subdomains. A platform might send with bounce.news.example.com in the envelope sender while the visible From domain is example.com. A transactional provider might sign with mail.example.com. Relaxed alignment lets these patterns work without turning every sender into a fragile exact-domain project.
- SPF can align when the MAIL FROM domain and From domain share the same organizational domain.
- DKIM can align when the validated d= domain and From domain share the same organizational domain.
- Either aligned pass is enough for DMARC to pass.
- This is the default when adkim and aspf are omitted.
Strict alignment requires an exact match
Strict alignment changes the comparison from “same organizational domain” to “same domain.” With aspf=s, SPF alignment requires the validated MAIL FROM domain to match the visible From domain exactly. With adkim=s, the validated DKIM d= domain must match exactly.
_dmarc.example.com. TXT "v=DMARC1; p=reject; adkim=s; aspf=s; rua=mailto:reports@example.net"Strict mode is not “more DMARC.” It is a narrower authorization model. It can be valuable for a tightly controlled domain, but it also removes a lot of legitimate subdomain-based flexibility. The most common mistake is enabling strict SPF alignment while a vendor still uses a subdomain return-path.
Why SPF alignment breaks more often
SPF authenticates the envelope sender domain, not the visible From domain. That envelope sender is often controlled by a sending platform because it needs to handle bounces, feedback loops, and mail stream routing. Even when the visible From address is hello@example.com, the SPF domain might be bounces.eu.vendor.example or bounce.mail.example.com.
If the bounce domain belongs to the vendor's organizational domain, SPF can pass but remain unaligned. That is expected. The fix is usually not a bigger SPF record. It is a domain-aligned return-path, or a reliable aligned DKIM signature.
- Find the visible From domain in the message header.
- Find the SPF-authenticated MAIL FROM or return-path domain.
- Check whether that domain belongs to your organizational domain.
- If it belongs to a vendor domain, configure a custom bounce domain or rely on aligned DKIM.
DKIM alignment is usually the safer anchor
DKIM survives forwarding better than SPF because the cryptographic signature can remain valid as the message moves through intermediaries. That makes DKIM alignment the more dependable path for many senders, especially newsletters, transactional mail, and tools that users forward internally.
The practical target is simple: every legitimate sender should produce at least one valid DKIM signature with a d= domain that aligns with the visible From domain. If the sender also has aligned SPF, great. If forwarding breaks SPF later, DMARC can still pass through DKIM.
When strict alignment is worth it
Strict alignment is useful when a domain has a deliberately small sender set and every sender can use the exact From domain for DKIM and SPF. Think executive-only domains, high-risk finance workflows, or tightly governed transactional domains where operational complexity is low and the blast radius of impersonation is high.
It is less useful as a broad default for a corporate root domain with many teams, regions, acquired systems, and SaaS tools. There, strict mode often turns into a breakage generator. Attackers are better blocked by moving to p=reject, keeping subdomain policy explicit, and closing unused domains than by surprising legitimate senders with exact-match requirements.
- Every important sender has aligned DKIM with the exact From domain, or can be changed safely.
- Bounce domains are either exact-match or SPF alignment is not needed for that mail stream.
- Forwarding, mailing lists, and helpdesk flows still have a DKIM-aligned pass path.
- The domain owner has a rollback plan if a critical vendor changes behavior.
The rollout pattern we recommend
Start with the default: relaxed adkim and relaxed aspf. Move the domain toward p=reject by fixing the senders that fail both authentication and alignment. Treat aligned DKIM as the primary success path for most third-party senders.
Once enforcement is stable, look for domains where strict alignment actually reduces risk without creating operational noise. Do it one domain at a time, watch aggregate reports, and measure whether failures are real abuse or just legitimate mail that used a subdomain.
Practical default:
v=DMARC1; p=reject; rua=mailto:reports@example.net

Selective strict mode:
v=DMARC1; p=reject; adkim=s; rua=mailto:reports@example.net
Notice that strict DKIM and strict SPF do not have to move together. If your DKIM signatures can be exact but your bounce handling still needs subdomains, adkim=s with the default relaxed aspf may be a better intermediate step than turning both knobs at once.
Where DMARCify fits
DMARCify helps separate authentication failures from alignment failures. That distinction is what tells you whether a sender needs SPF authorization, DKIM configuration, a custom bounce domain, or a strict-alignment exception.
The clean operating rule is: keep relaxed alignment as the default, make every legitimate sender pass through aligned DKIM or SPF, and reserve strict alignment for domains where the reports prove exact matching is already true.
Disclosure: AI tools were used in the process of creating this blog post.